There are definitely more reasons to use Cloudflare for WordPress websites these days than there used to be, especially with the increasing use of AI for malicious purposes.
No matter how fast and secure your hosting provider’s infrastructure, your web site’s reliability depends on what you put on top of that.
You can notice that how frequent WordPress core updates (maintenance updates) has become to cope with these new vulnerabilities that are discovered almost everyday.
Since WordPress is still powers almost half of the websites on the internet, it is by far one the most targeted platforms amongst hackers.
In this step-by-step guide, you’ll learn how to set up Cloudflare for your WordPress website, improve load times, protect against security threats, and improve its reliability.
What is Cloudflare?
At its core, Cloudflare is a global network that sits in front of your website.
It speeds up your site by serving files from data centers close to your visitors. These data centers are called edge locations, and together they make up Cloudflare’s “edge.”
It also protects your site by filtering out harmful traffic before it reaches your origin server. The origin server is where your website is actually hosted.
Why Use Cloudflare with WordPress?
Your hosting provider handles the server. Cloudflare handles everything that tries to reach it. Here’s what that means for a WordPress site, today.
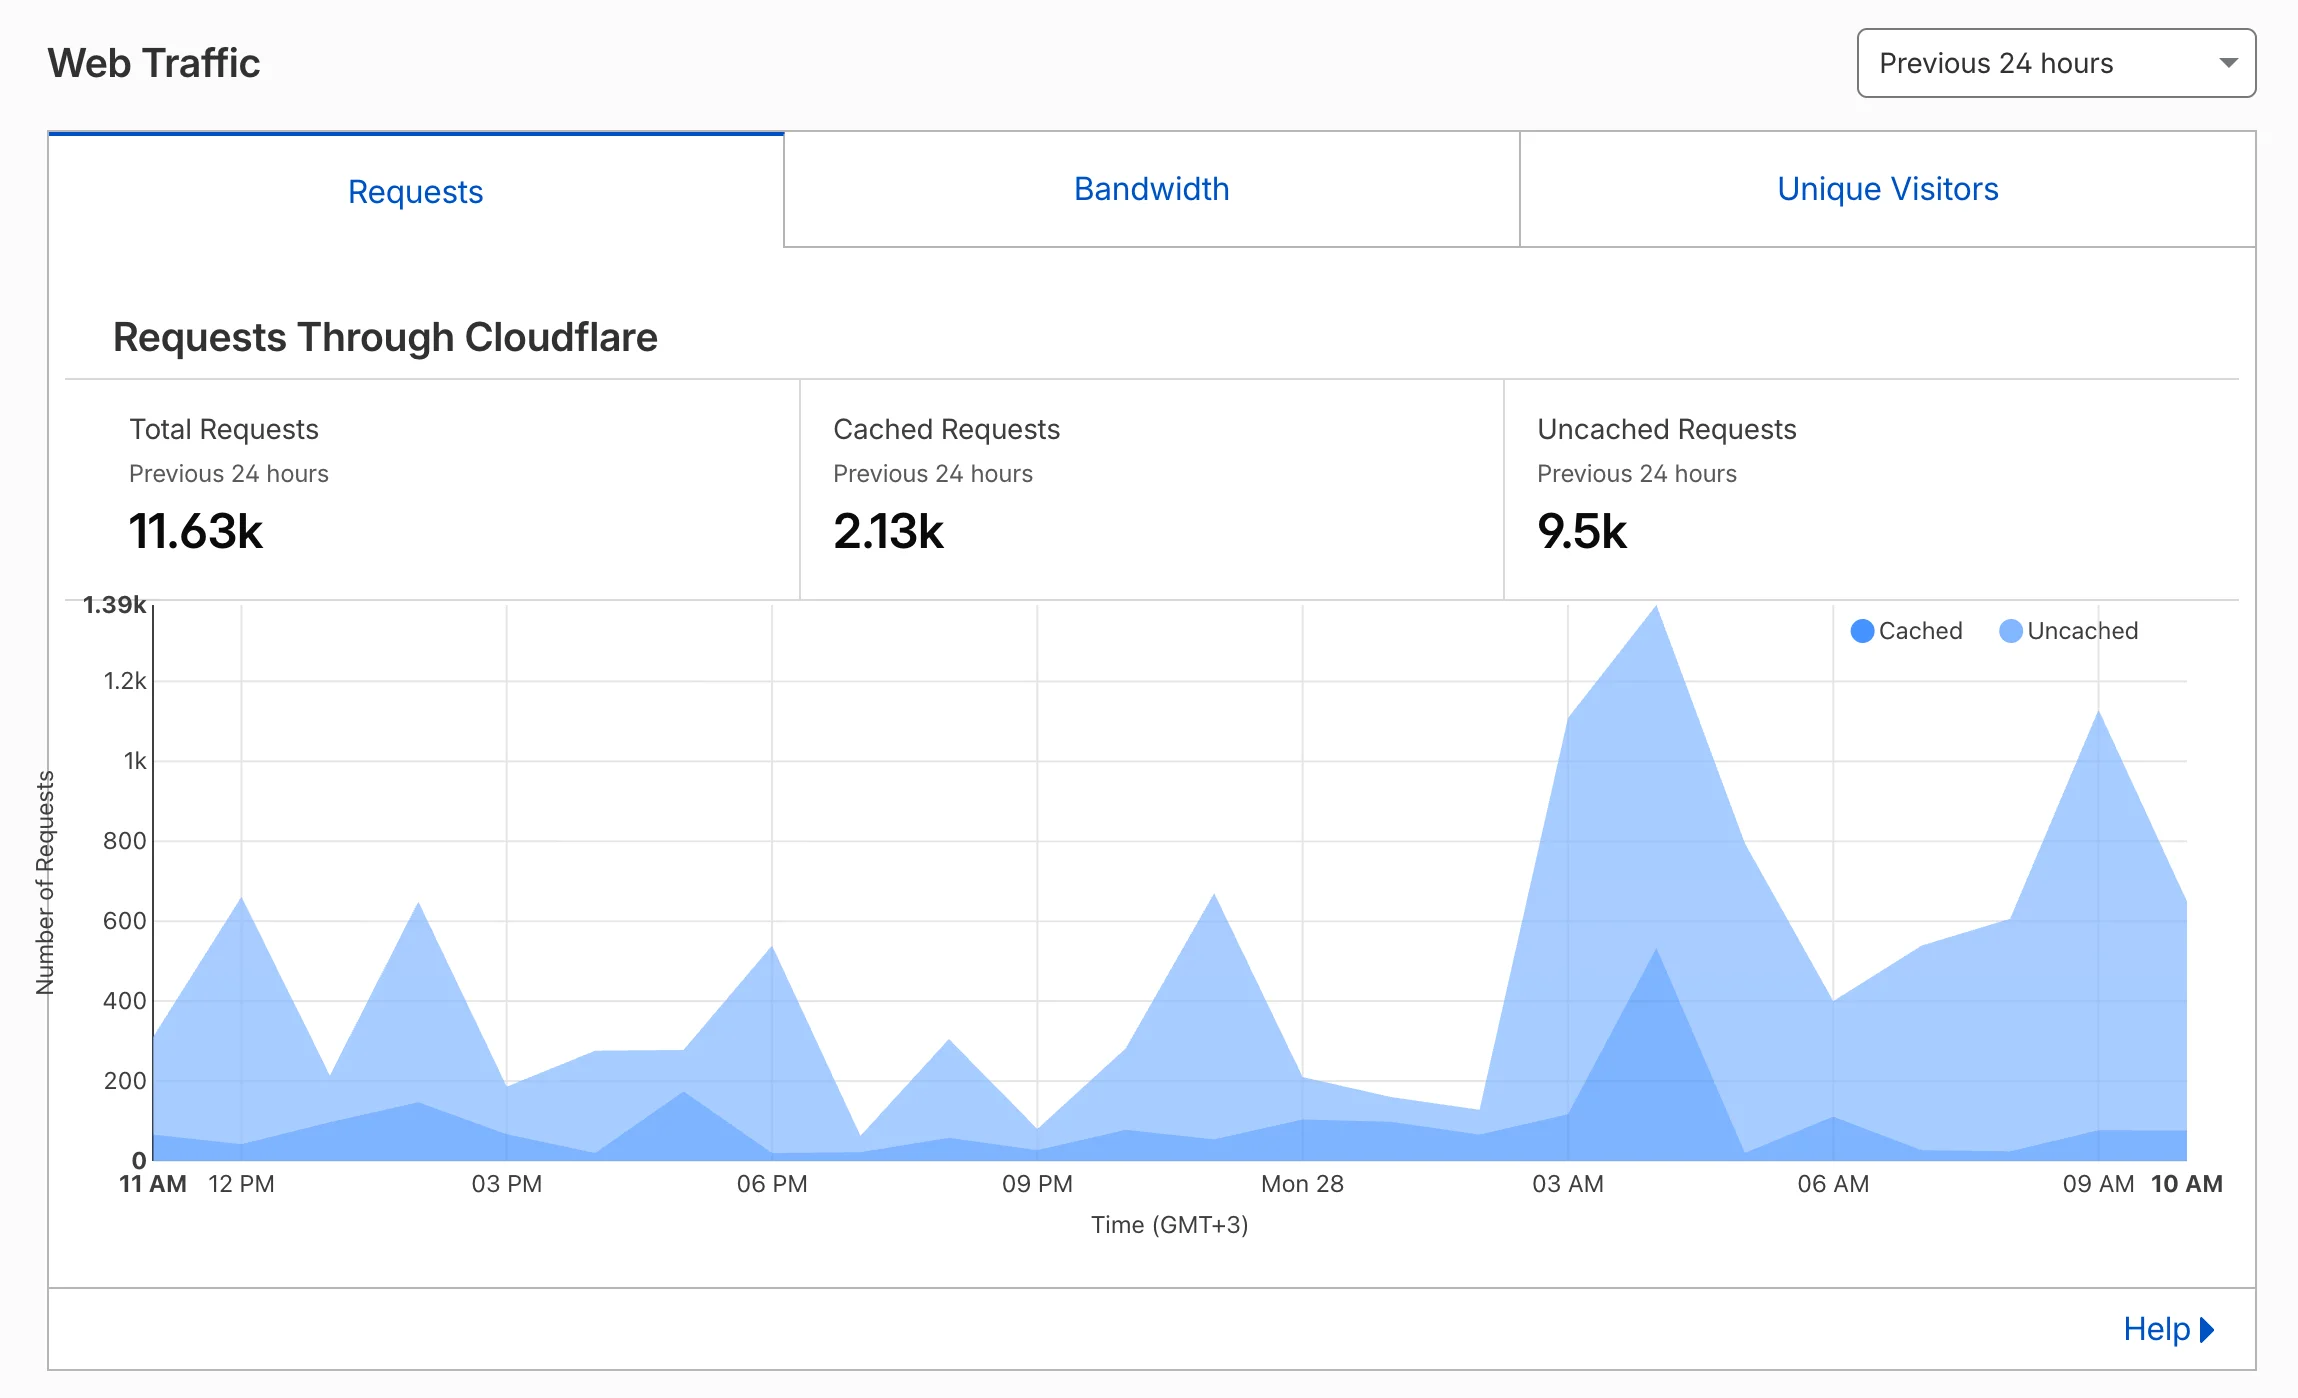
- Faster load times worldwide. Cloudflare serves your images, CSS, JavaScript, and fonts from edge locations close to your visitors. By default, it does not cache your HTML pages. You can enable full-page caching with Cache Rules for bigger gains and preload your pages on Cloudflare edge network to improve TTFB (time to first byte) even further.
- Less work for your origin server. Every cached file is one less request your server has to handle. This frees up resources for the requests that matter, like logged-in users and pages that can not be cached.
- Protection from vulnerability scans. Bots probe WordPress sites all day long, almost every second, for weak plugins, exposed files, and login pages. Many of these scans now use AI to find and exploit flaws within hours of disclosure. Cloudflare’s custom firewall rules let you block these requests before they ever reach WordPress.
- Control over AI crawlers. AI companies crawl websites to train their models. Some crawl aggressively and ignore robots.txt. Cloudflare lets you block them with a single toggle.
- Bot and DDoS protection. Cloudflare filters out known bad bots and absorbs DDoS attacks on its own network. Search engine crawlers and other good bots still get through.
- A hidden origin IP. Visitors and attackers only see Cloudflare’s IP addresses. This makes it much harder to target your server directly.
- Free SSL and HTTPS. Cloudflare issues a free SSL certificate for your domain. To also encrypt traffic between Cloudflare and your server, use “Full” or “Full (strict)” mode. Full accepts any certificate on your server. Full (strict) requires a valid one and is more secure. Cloudflare’s free Origin CA certificate works with Full (strict) and lasts up to 15 years, since only Cloudflare needs to trust it. Install it once and forget about renewals.
- Better Core Web Vitals. Time to First Byte (TTFB) is usually the biggest part of Largest Contentful Paint (LCP). Caching your HTML at the edge with Cache Rules can cut TTFB to under 100 ms. This one change often brings the biggest LCP improvement.
Best of all, every feature above is included in Cloudflare’s free plan. You don’t need a paid subscription to get faster load times and solid protection for your WordPress site.
How to Set Up Cloudflare on WordPress (Step-by-Step)
Putting Cloudflare in front of your site is easier than you might think.
During setup, Cloudflare gives you two nameservers. You replace your current nameservers with these at your domain registrar. From then on, Cloudflare manages your domain’s DNS.
1. Create a Free Cloudflare Account
- Go to https://www.cloudflare.com
- Click Sign Up and create your account
- Enter your domain (e.g., yourdomain.com)
2. Scan Your DNS Records
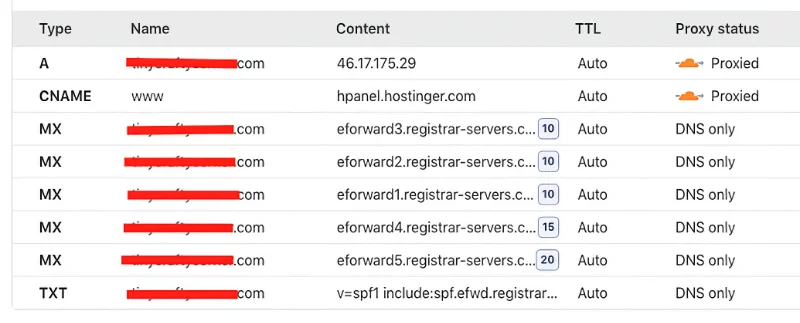
- Cloudflare will automatically scan your existing DNS records
- Review the records and ensure everything is correct
- Click Continue
You will see a similar screen to the one below. Proxied means that the traffic will go through Cloudflare network.
3. Update Nameservers
- Cloudflare will provide you with two new nameservers
- Log in to your domain registrar (e.g., GoDaddy, Namecheap, etc.)
- Replace the current nameservers with the ones provided by Cloudflare
- Save changes and wait for propagation (usually within an hour)
4. Configure SSL Settings (optional)
- In your Cloudflare dashboard, go to SSL/TLS
- SSL mode defaults to Full, which is enough for your visitors to access your site securely via HTTPS.
- Enable Always Use HTTPS and Automatic HTTPS Rewrites
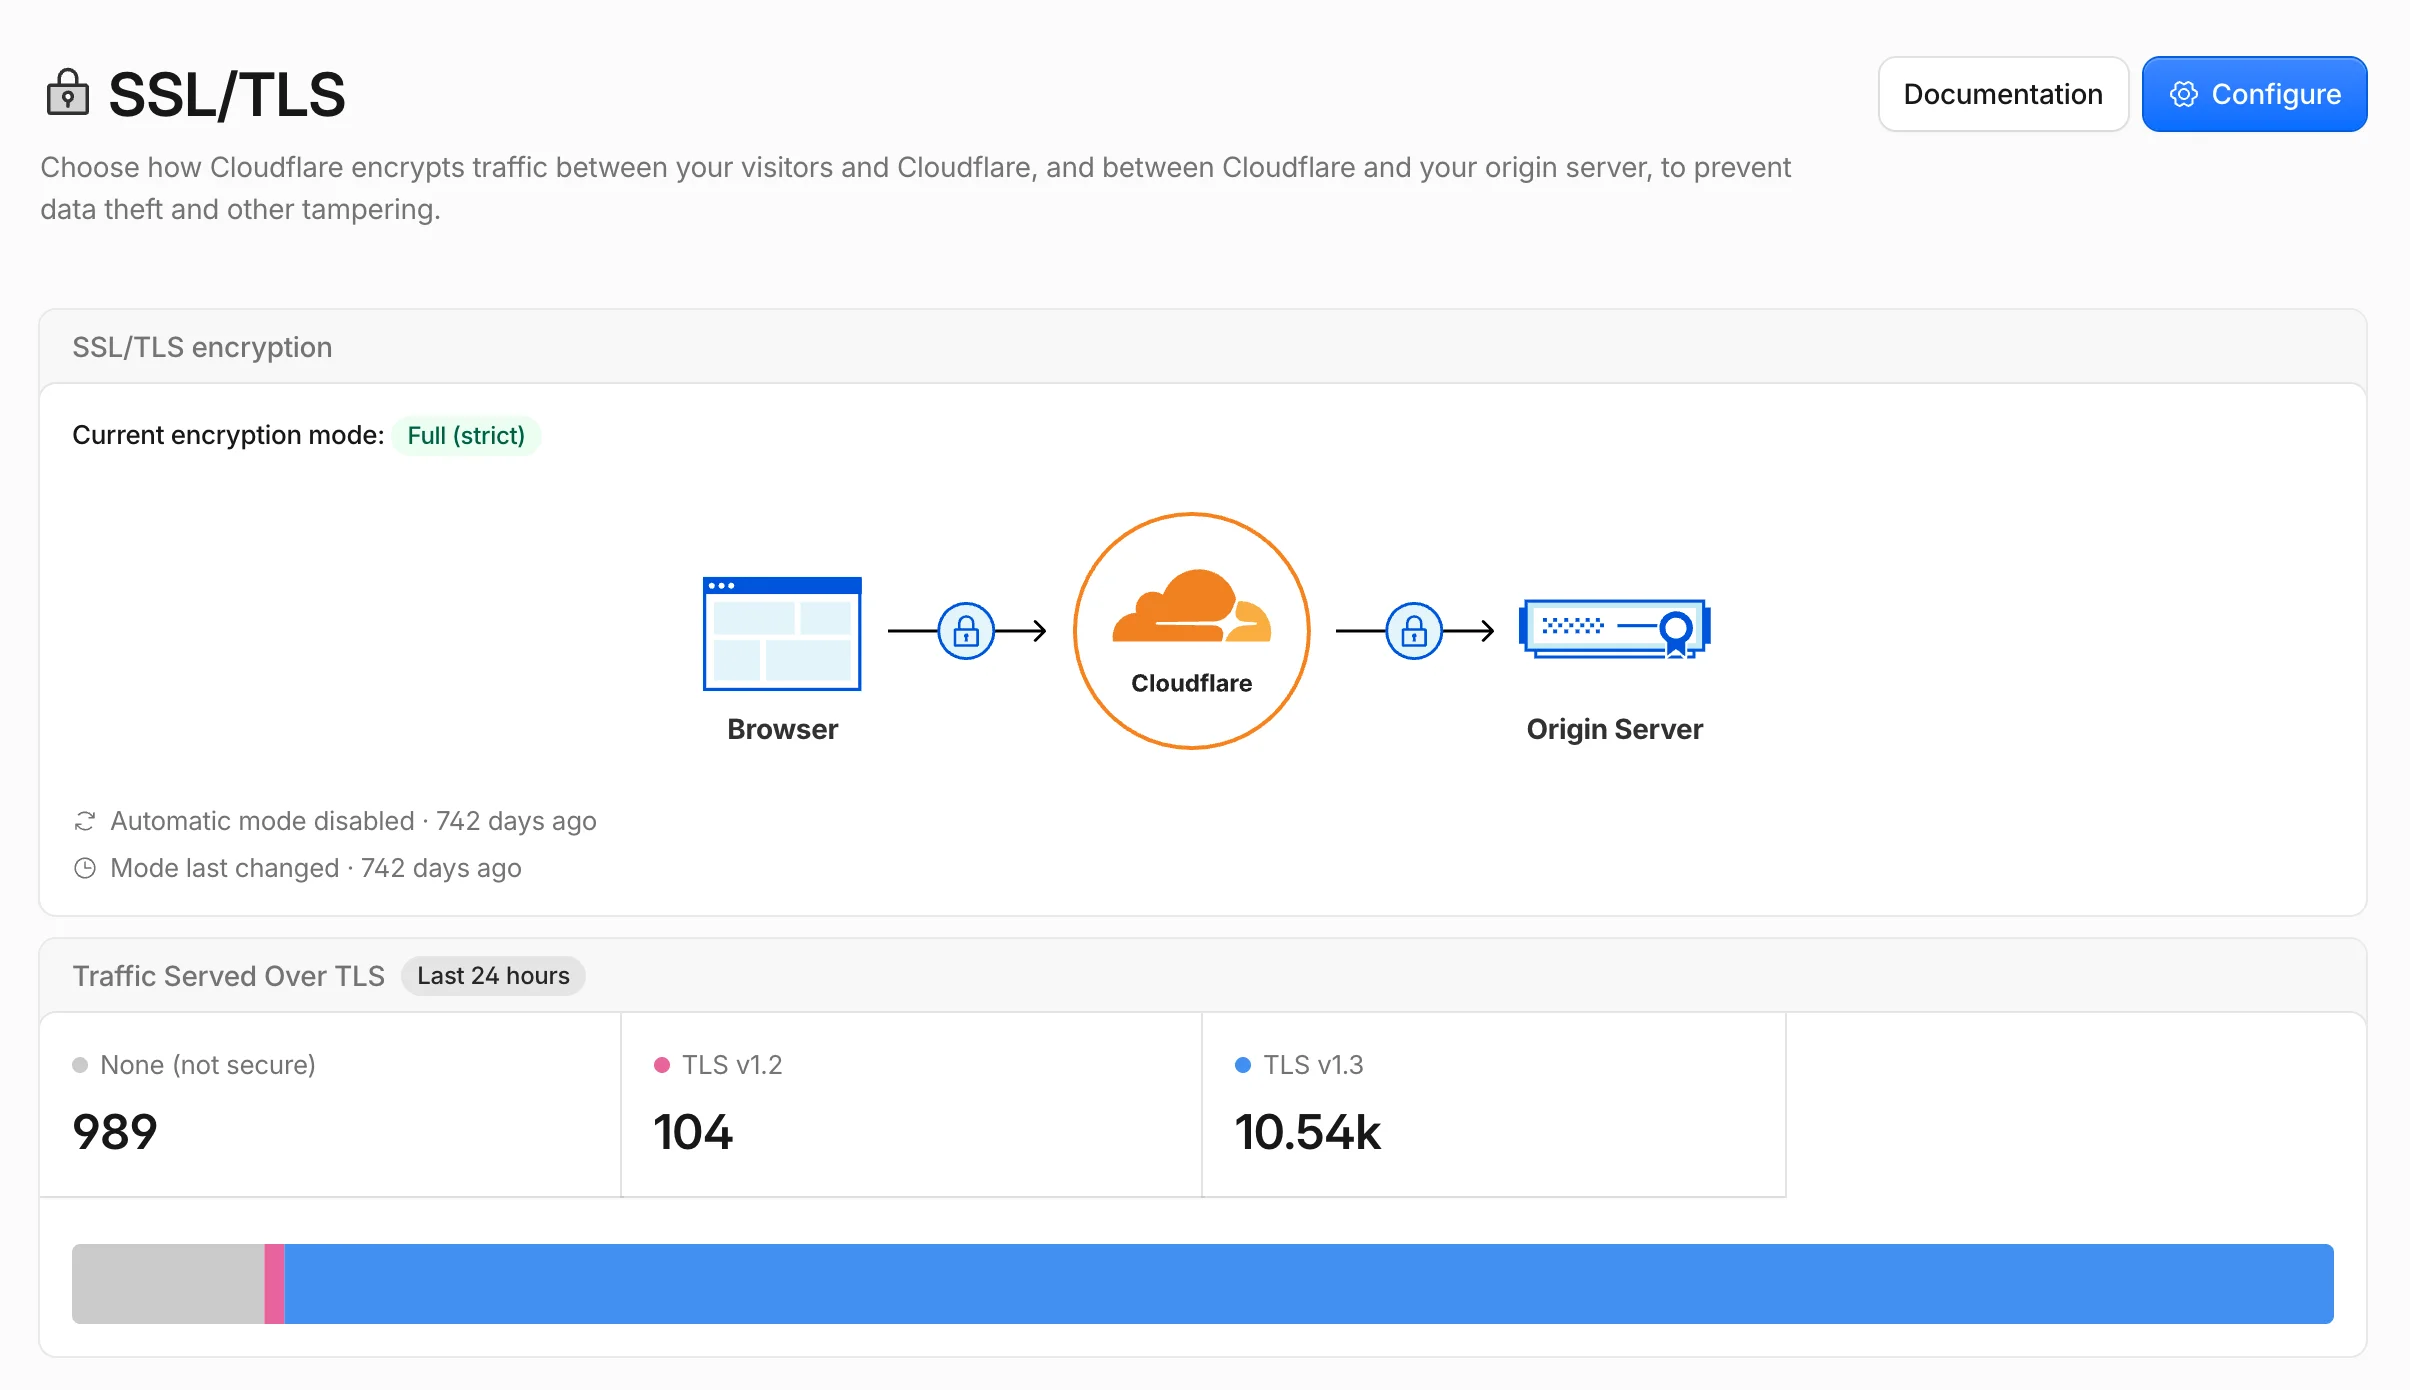
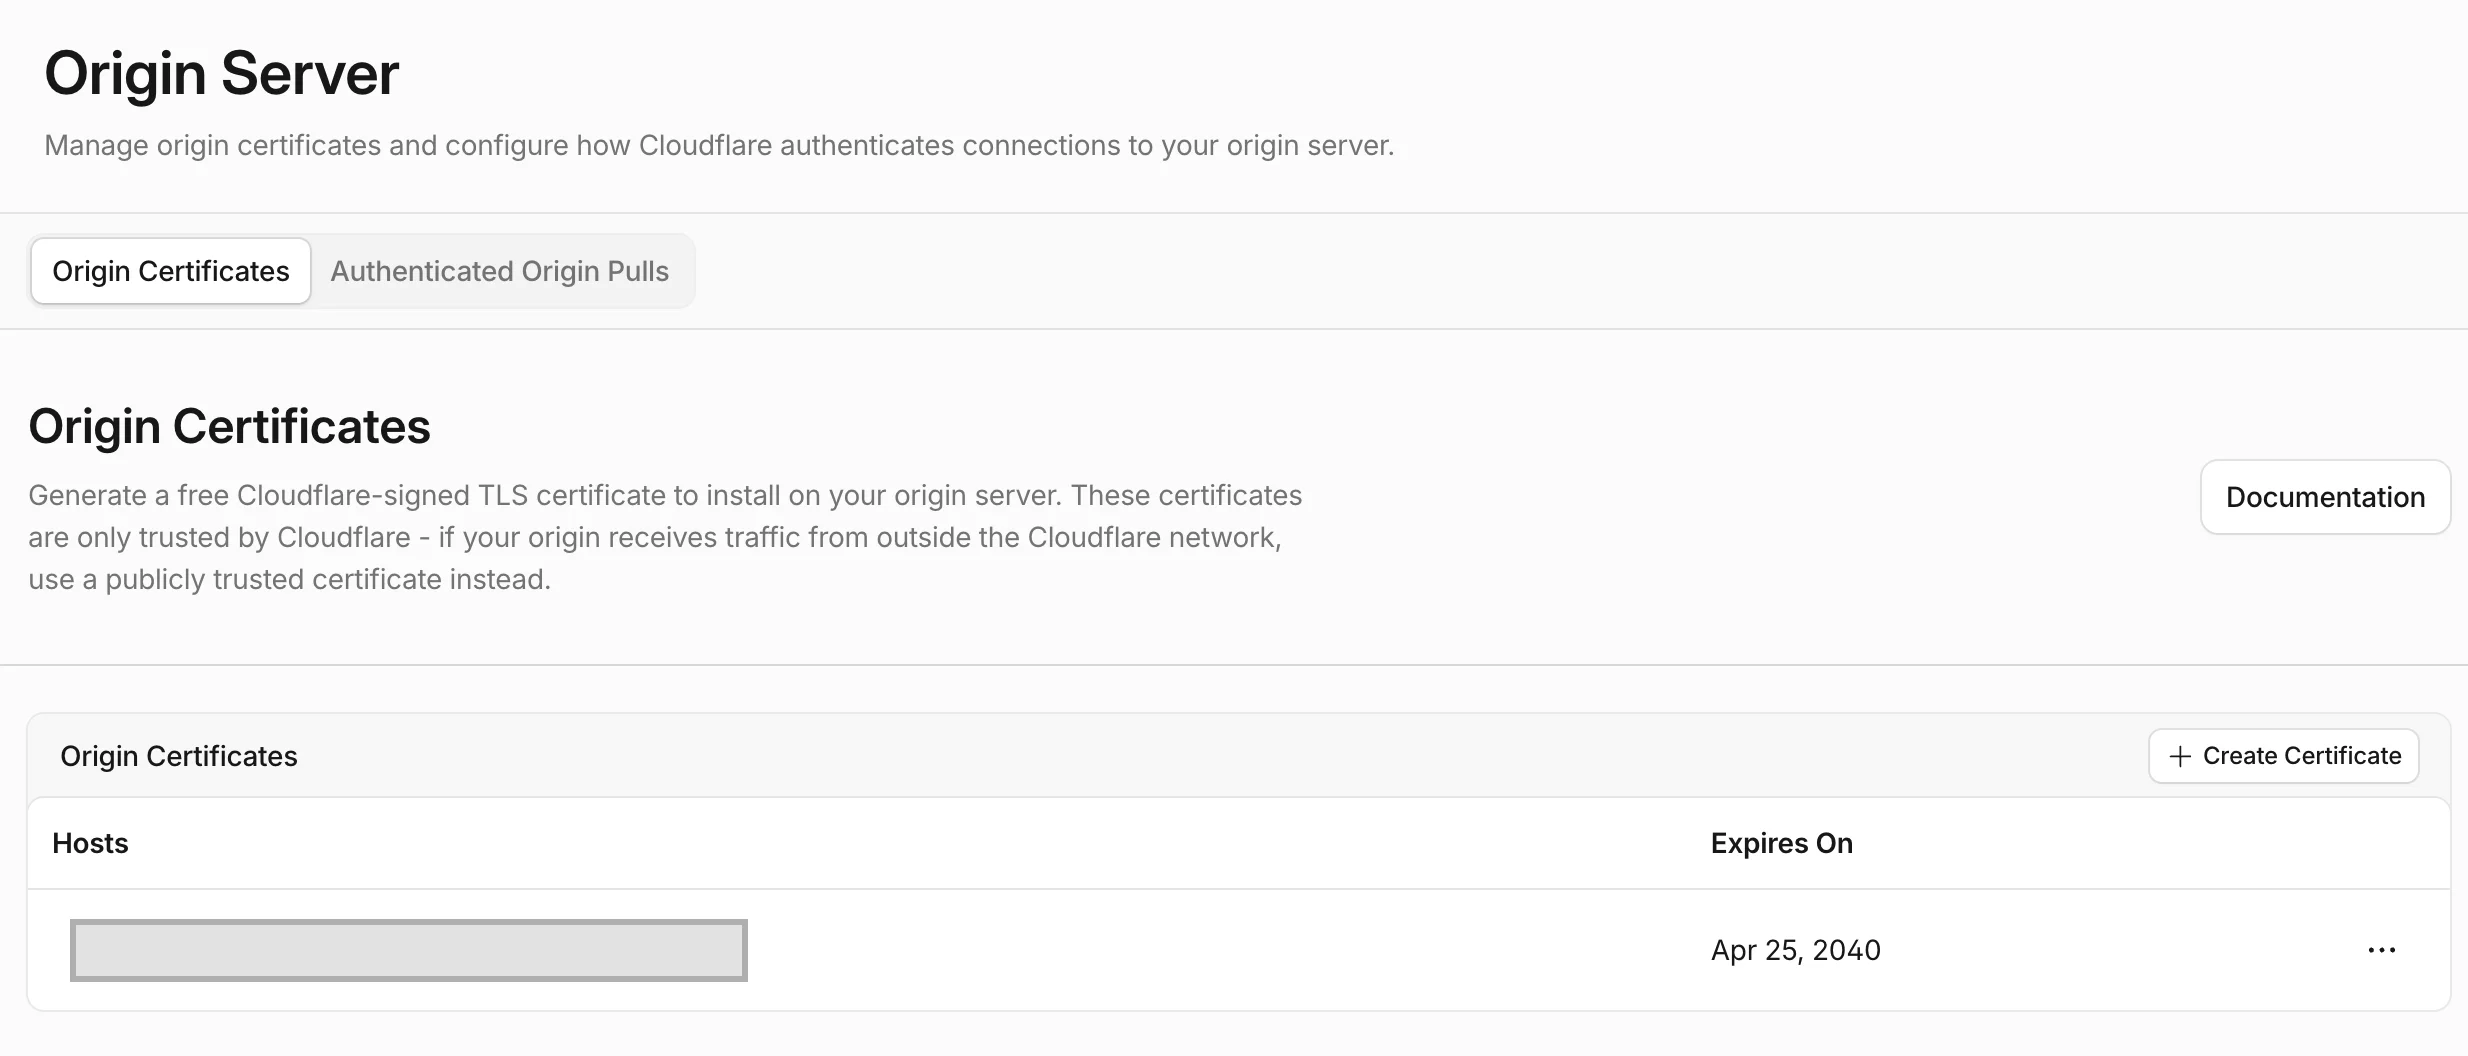
Tip: If you want to make the connection between Cloudflare and your origin server secure, you can set the mode to Full Strict. Cloudflare provides free Origin SSL (valid for 15 years) for this purpose.
You can install it on your origin server through your own hosting control panel.
Don’t use Let’s Encrypt or similar on the origin server as they won’t be able to auto-renew while your domain points to Cloudflare nameservers.
5. Install a Cloudflare Plugin for WordPress
You can either choose to use the official plugin, or install the Super Page Cache plugin (my preferred choice).
I like to use Super Page Cache (free version) because it creates and manages Cache Rules that cache full HTML pages at Cloudflare’s edge. It also purges the cache automatically when you update content and bypasses dynamic pages like cart, checkout, and wp-admin.
The official Cloudflare plugin offers full-page caching only through Automatic Platform Optimization (APO), which costs $5 per month on the free plan.
- From your WordPress dashboard:
- Go to Plugins > Add New
- Search and install your preferred Cloudflare plugin
- Activate it and connect to your Cloudflare account using API token as instructed by the plugin
Super Page Cache vs Cloudflare APO
Cloudflare’s Automatic Platform Optimization (APO) for WordPress is a paid feature that caches full HTML pages at Cloudflare’s edge.
It costs $5 per month per domain on the free plan and is included in Pro and higher plans. Super Page Cache does the same core job for free by creating Cache Rules on your Cloudflare account.
Both purge the cache automatically when you update content. Both skip logged-in users and dynamic pages like the cart, checkout, and account area. Both can cut your TTFB dramatically on cached pages.
The main difference is how cached pages reach each edge location.
APO stores your cached pages across Cloudflare’s wider network, so edge locations can serve them without asking your server first. This means visitors in quieter regions get fast responses more often.
With Super Page Cache, each edge location caches a page only after someone in that region requests it. Until then, visitors in less busy locations still wait for your origin server.
Super Page Cache has a built-in preloader, but it sends requests from your own server. That only warms the edge location closest to your server, not the ones near your visitors.
This is the gap our plugin, Super Preloader for Cloudflare, is built to close.
It warms up Cloudflare edge caches by preloading your public URLs using a Worker script and optional rotating Webshare proxies.
By sending requests from different locations around the world, it fills the cache at many edge locations before real visitors arrive.
Super Page Cache decides what gets cached and when it gets purged. Super Preloader makes sure those cached pages are ready in the regions where your visitors are.
Together, they bring you close to APO’s global coverage without the monthly fee.
Super Page Cache with Super Preloader is a great fit if you:
- Manage several sites and don’t want to pay $5 per month for each one
- Want full control over cache rules, exclusions, and preload schedules
- Have visitors spread across a few key regions and want those edges always warm
- Are comfortable deploying a Cloudflare Worker
APO is the better choice if you:
- Prefer a set-and-forget setup with no extra plugins or Workers
- Have a truly global audience with low traffic per region
- Already pay for a Cloudflare Pro plan, where APO is included
For most small and medium WordPress sites, Super Page Cache delivers APO-level speed for free. Adding Super Preloader extends that speed to visitors far from your server.
My Custom WAF Rules for Improved WordPress Security
I have been working with WordPress and Cloudflare for years, and these are the custom WAF rules I apply to almost every site I manage.
They block the most common attacks before they ever reach WordPress. All of them work on Cloudflare’s free plan, which allows up to five custom rules.
1. Blocking Rules
This rule blocks two of the most scanned endpoints on WordPress sites: xmlrpc.php and the REST API batch endpoint targeted by the wp2shell vulnerability.
Unless you’re using apps like Jetpack or the WordPress mobile app, xmlrpc.php should be blocked. It’s an old API that most sites no longer need.
Attackers use it for brute-force login attempts, since a single request can test hundreds of passwords.
The wp2shell vulnerability is a newer and more serious threat. It combines an SQL injection in the WP_Query class (CVE-2026-60137) with a bug in the REST API batch endpoint (CVE-2026-63030).
The entry point is the batch processing endpoint at /wp-json/batch/v1.
Attackers are scanning the internet for vulnerable sites, uploading malicious plugins and web shells, creating admin accounts, and running remote commands.
This vulnerability is fixed in WordPress versions 6.8.6, 6.9.5, 7.0.2, or newer, but attackers still probe for it on every site they find. Each of these requests reaches WordPress and PHP, which costs CPU time and slows your server for real visitors.
Blocking them at Cloudflare’s edge stops this waste before it ever reaches your origin server.
Steps:
- Log into your Cloudflare Dashboard
- Go to Security > Security Rules
- Click Create rule
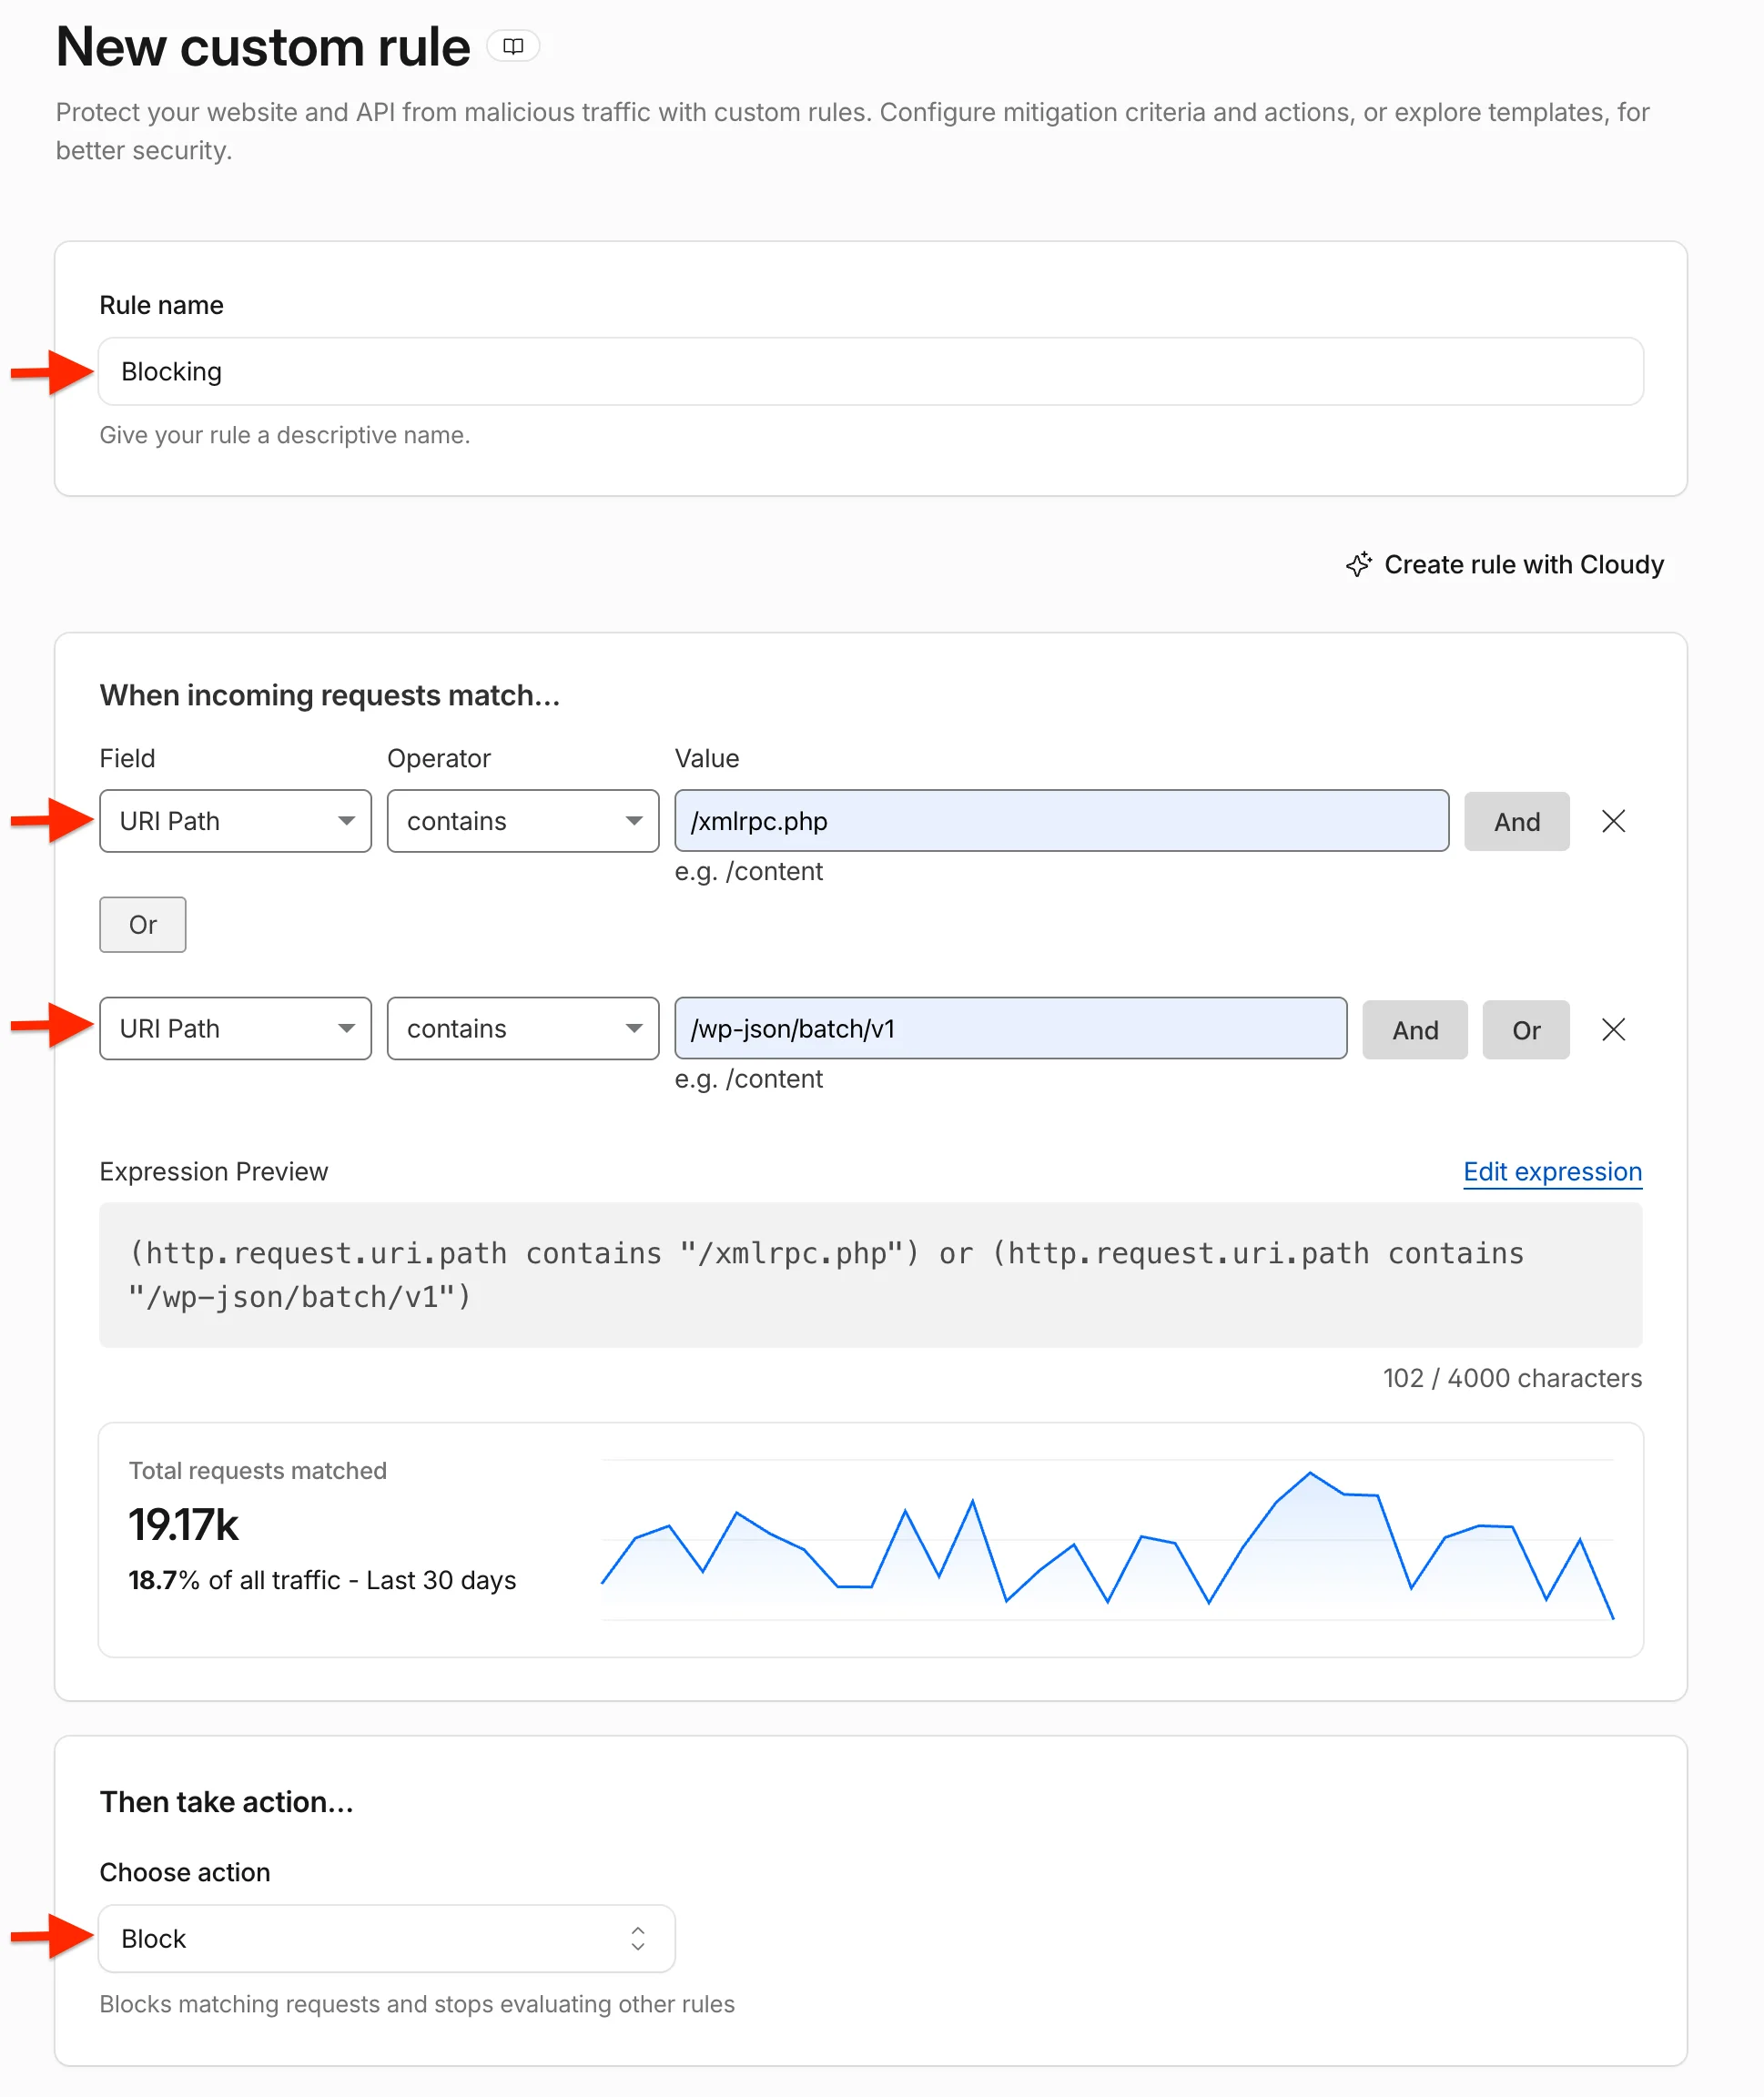
- Enter any rule Name (e.g. Blocking)
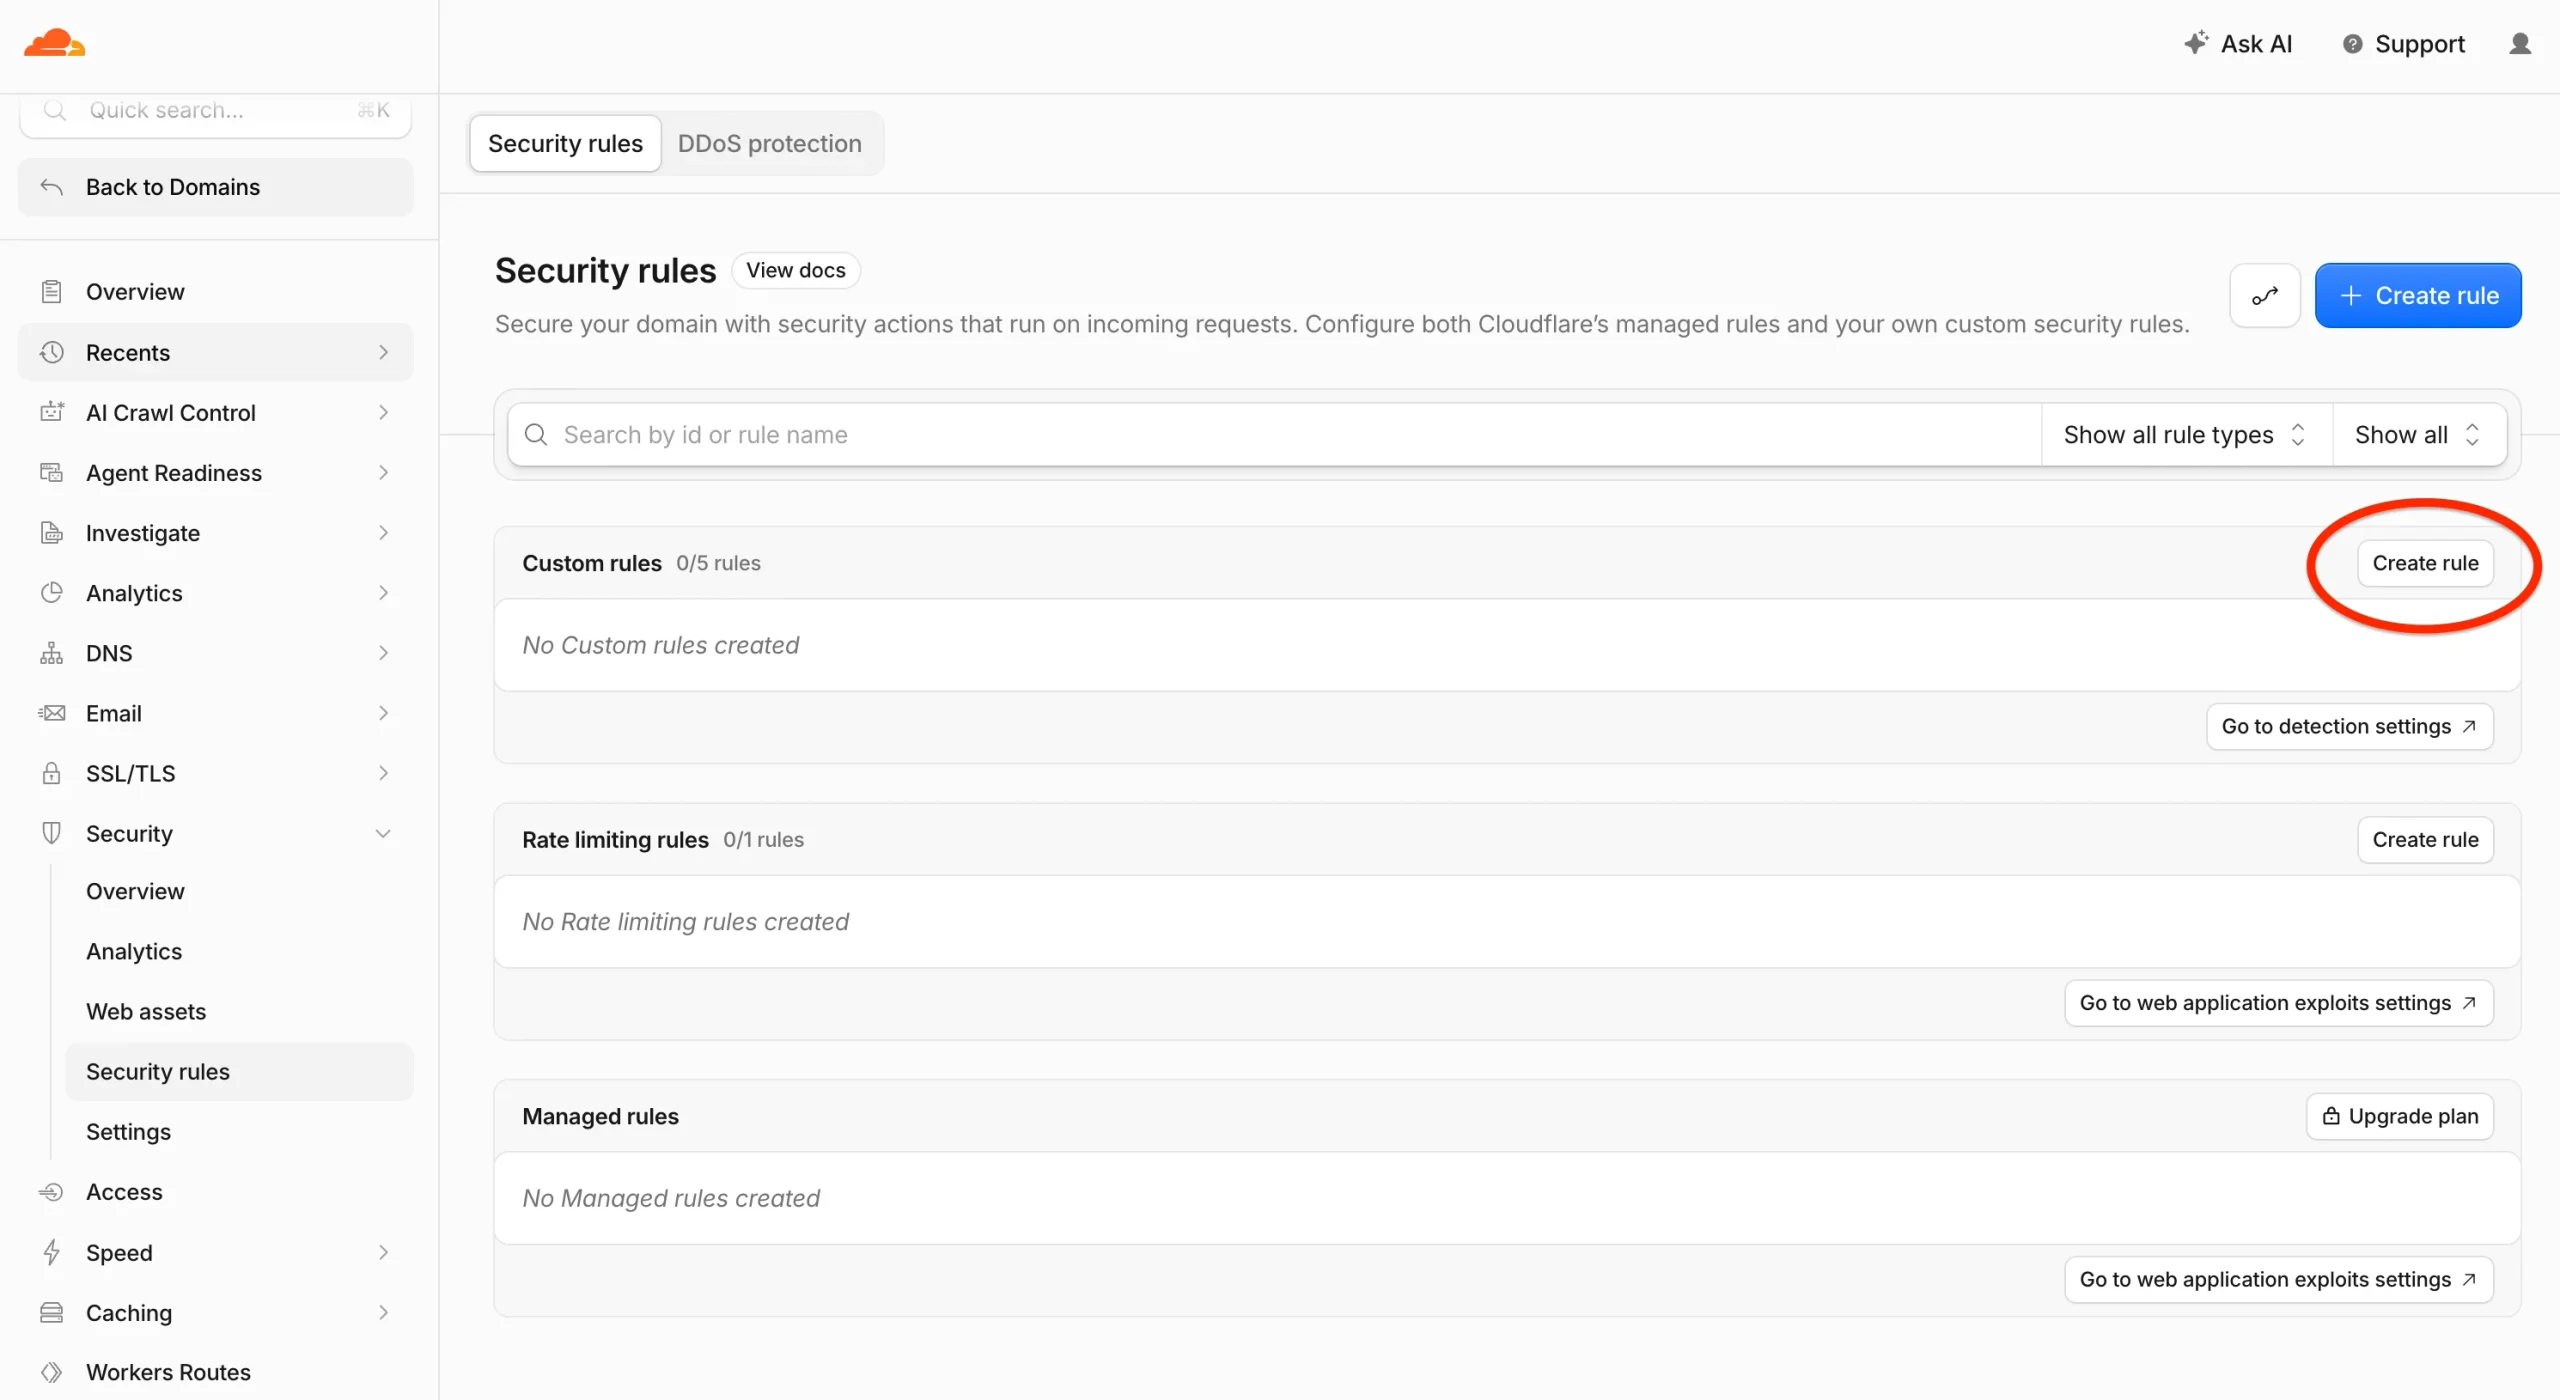
Cloudflare Security Rules
Fill out the form as in the sample rule set below
- URI Path > contains >
/xmlrpc.php - URI Path > containst >
/wp-json/batch/v1 - Choose action: Block
- Click Deploy to save
Your site is now protected from xmlrpc based exploits and wp2shell attacks.
2. Managed Challenge Rules
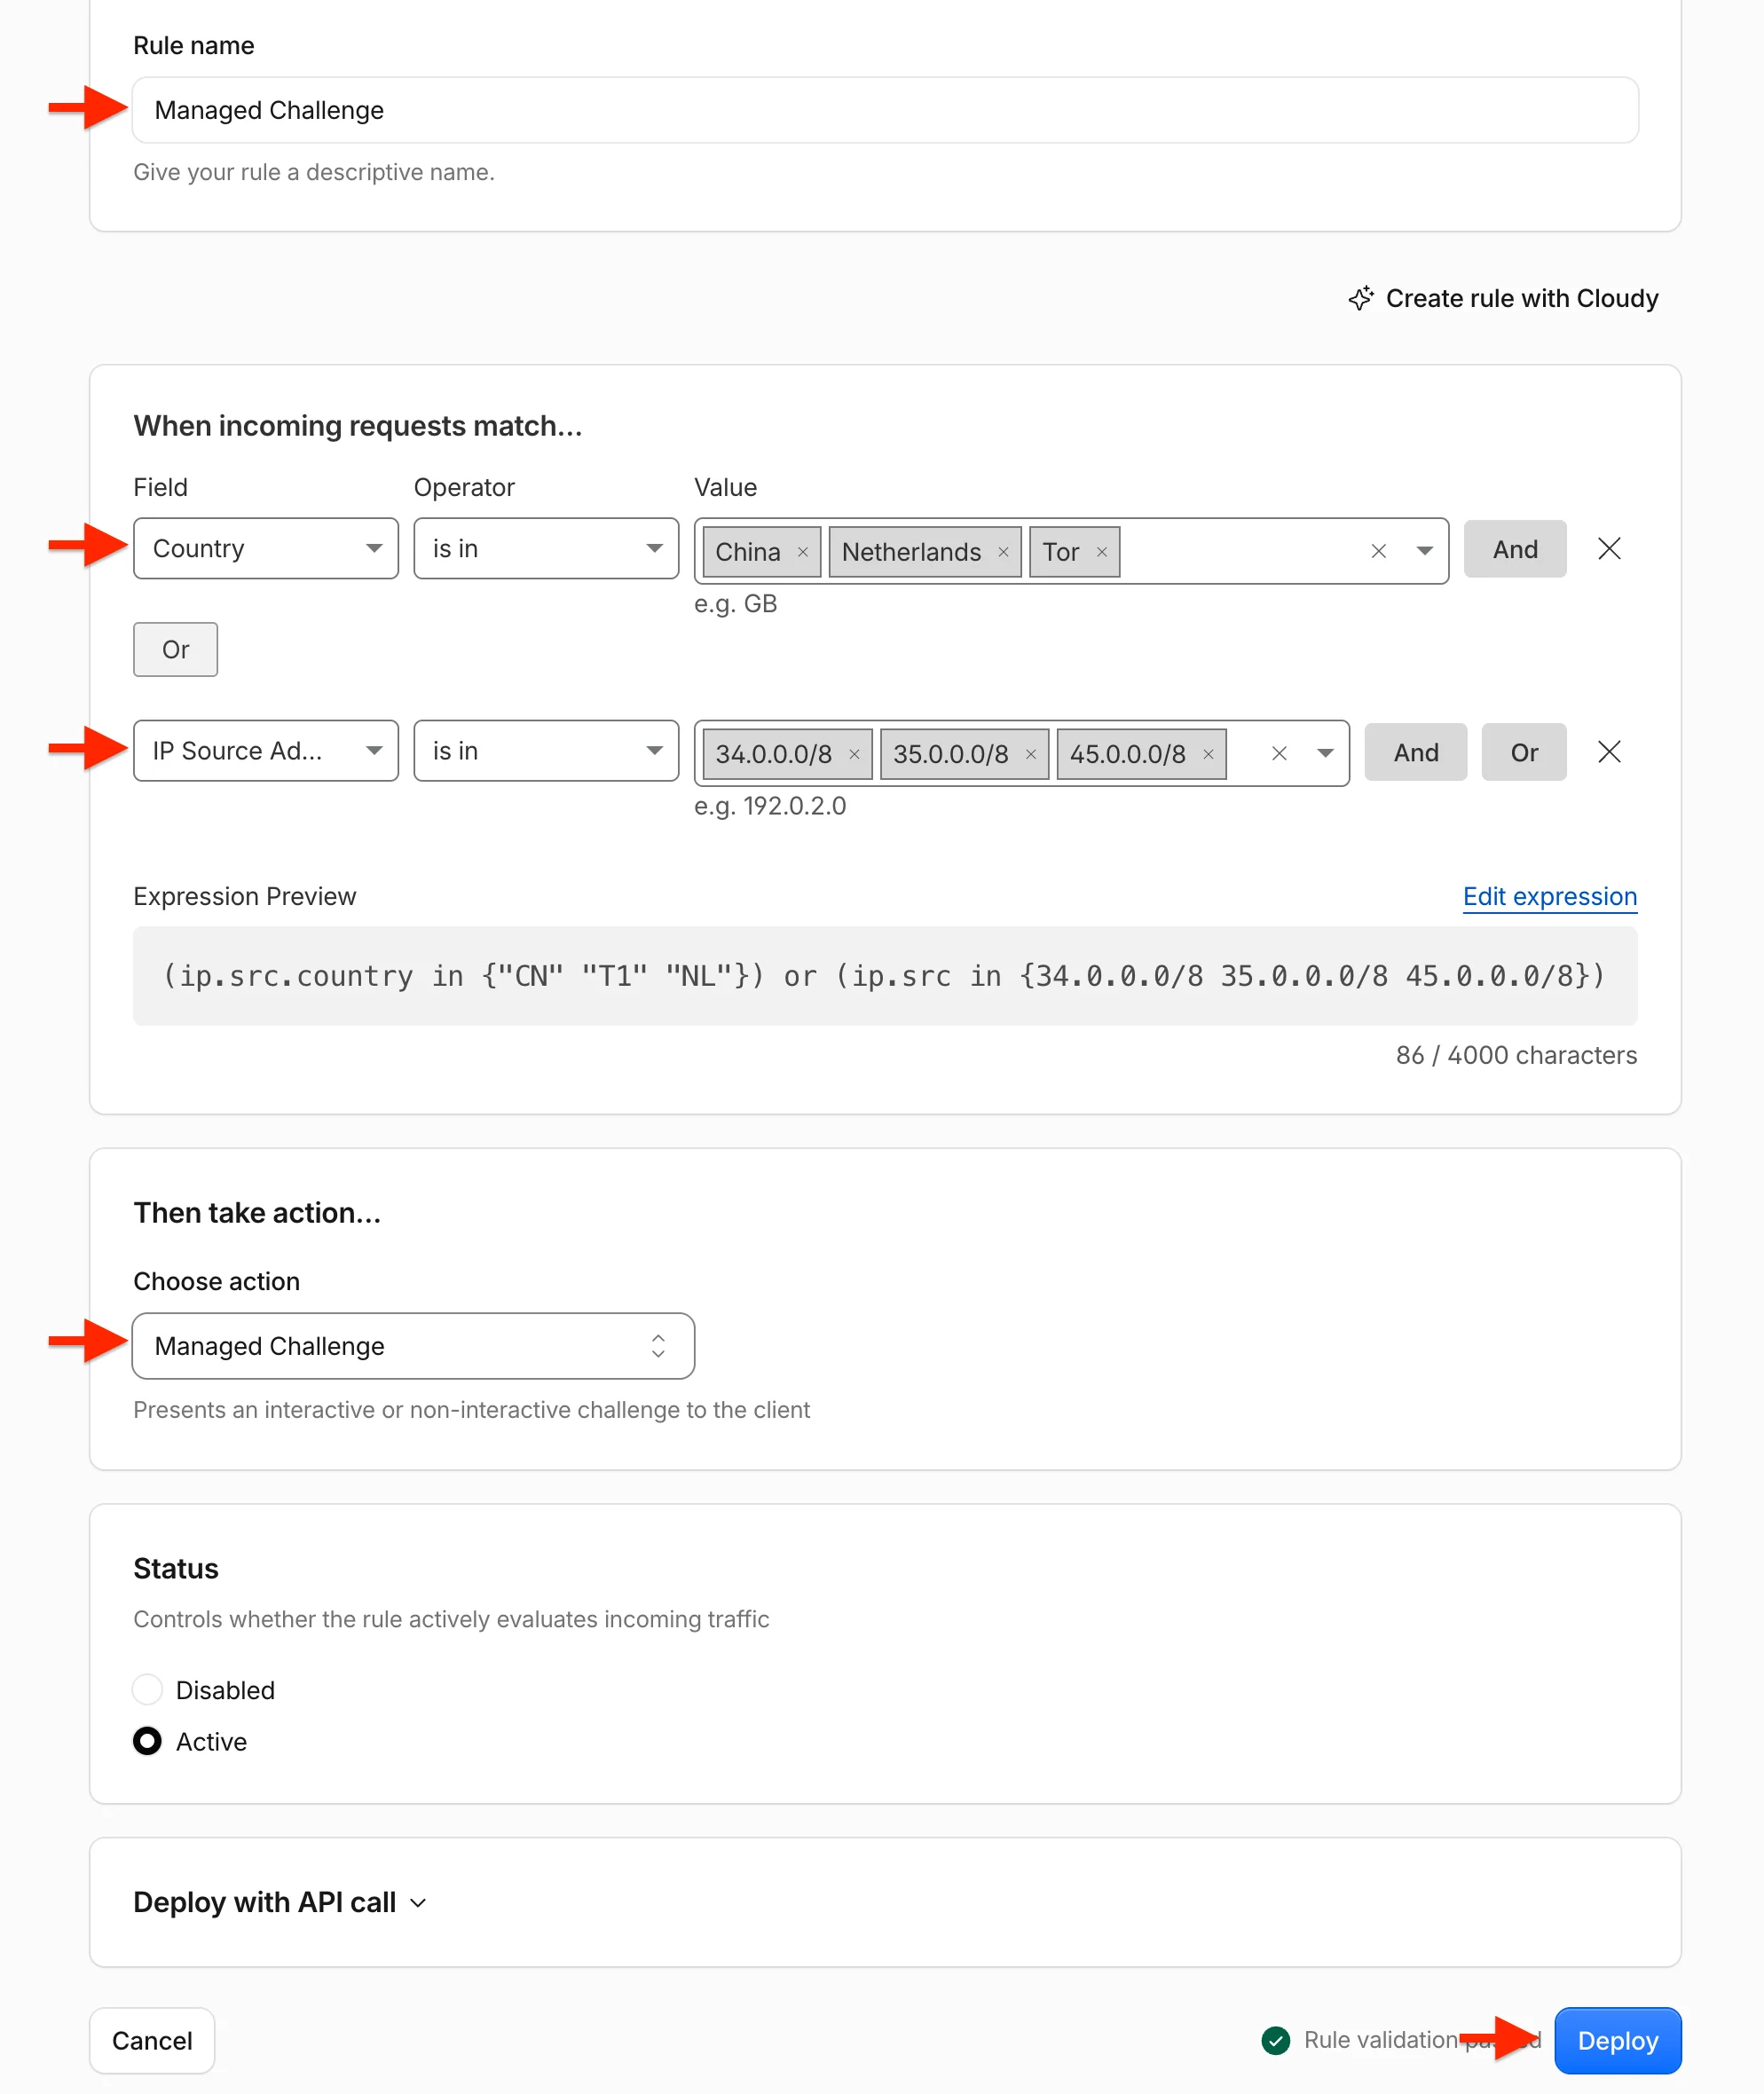
I like to use Managed Challenge rules to filter traffic from countries or networks where most probing bots come from.
Managed Challenge doesn’t block visitors outright. Cloudflare runs a quick check in the browser, and most real visitors pass without even clicking anything. Automated scripts usually fail and never reach your site.
From my experience, vulnerability scanning bots usually originate from the following countries and IP blocks.
Countries:
- Tor (Onion network)
- Netherlands
- Germany
- France
- China
- Russian Federation
- South Korea
- Mexico
- India
- Singapore
- Taiwan
- Switzerland
- United Arab Emirates
- Hong Kong
- Lithuania
IP Blocks:
- 34.0.0.0/8
- 35.0.0.0/8
- 45.0.0.0/8
- 20.0.0.0/8
You can fine tune these based on your real traffic and your target audience which you can monitor using the Security > Analytics tab at your Cloudflare dashboard.
To add a Manager Challenge rule, click the same Create Rule button you have clicked as the Blocking rules.
Steps:
- Country > is in > Type in countries
- IP Source Address > is in > Type in individual IPs or preferably IP blocks (e.g. 34.0.0.0/8 means all IPv4 IP addresses that start with 34)
- You may add extra OR cases here if you notice any other pattern of requests coming from bots
- Choose action: Managed Challenge
- Click Deploy to save
Make sure to monitor your traffic using the Security > Analytics tab of Cloudflare and fine tune these later on.
You will be amazed to see the endpoints they are trying to reach, from .env files to all sorts of configuration files, searching for a left over file that might contain sensitive login credentials.
3. Rate Limiting Rules
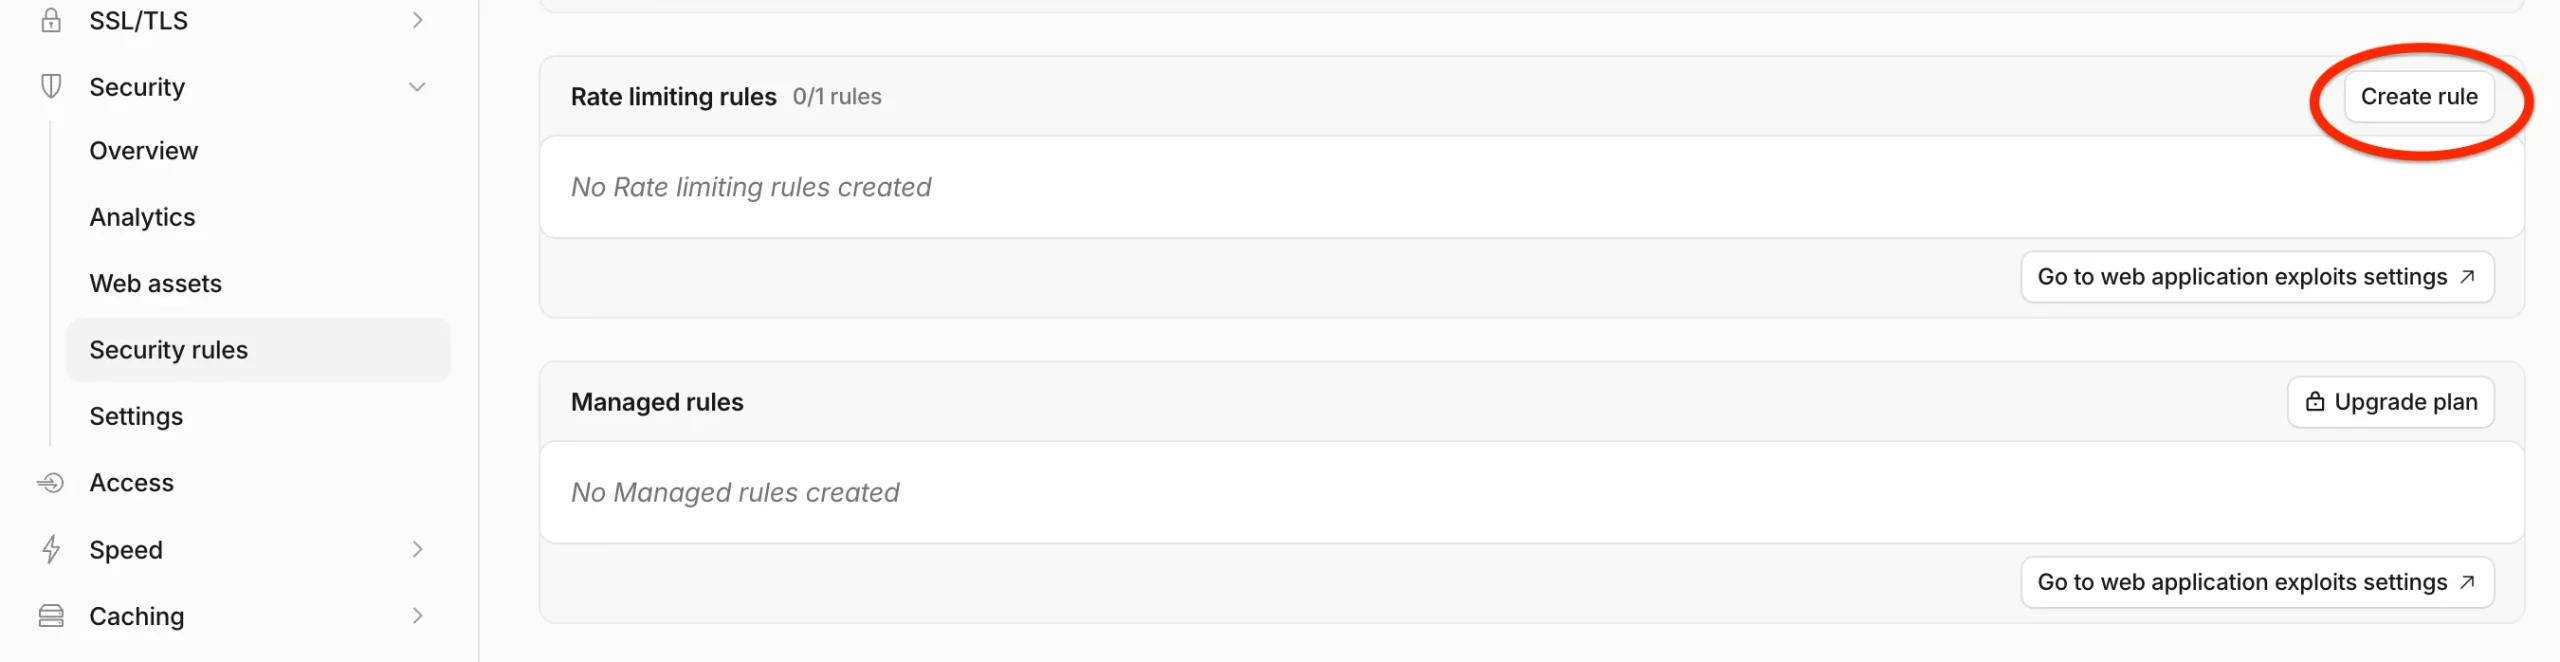
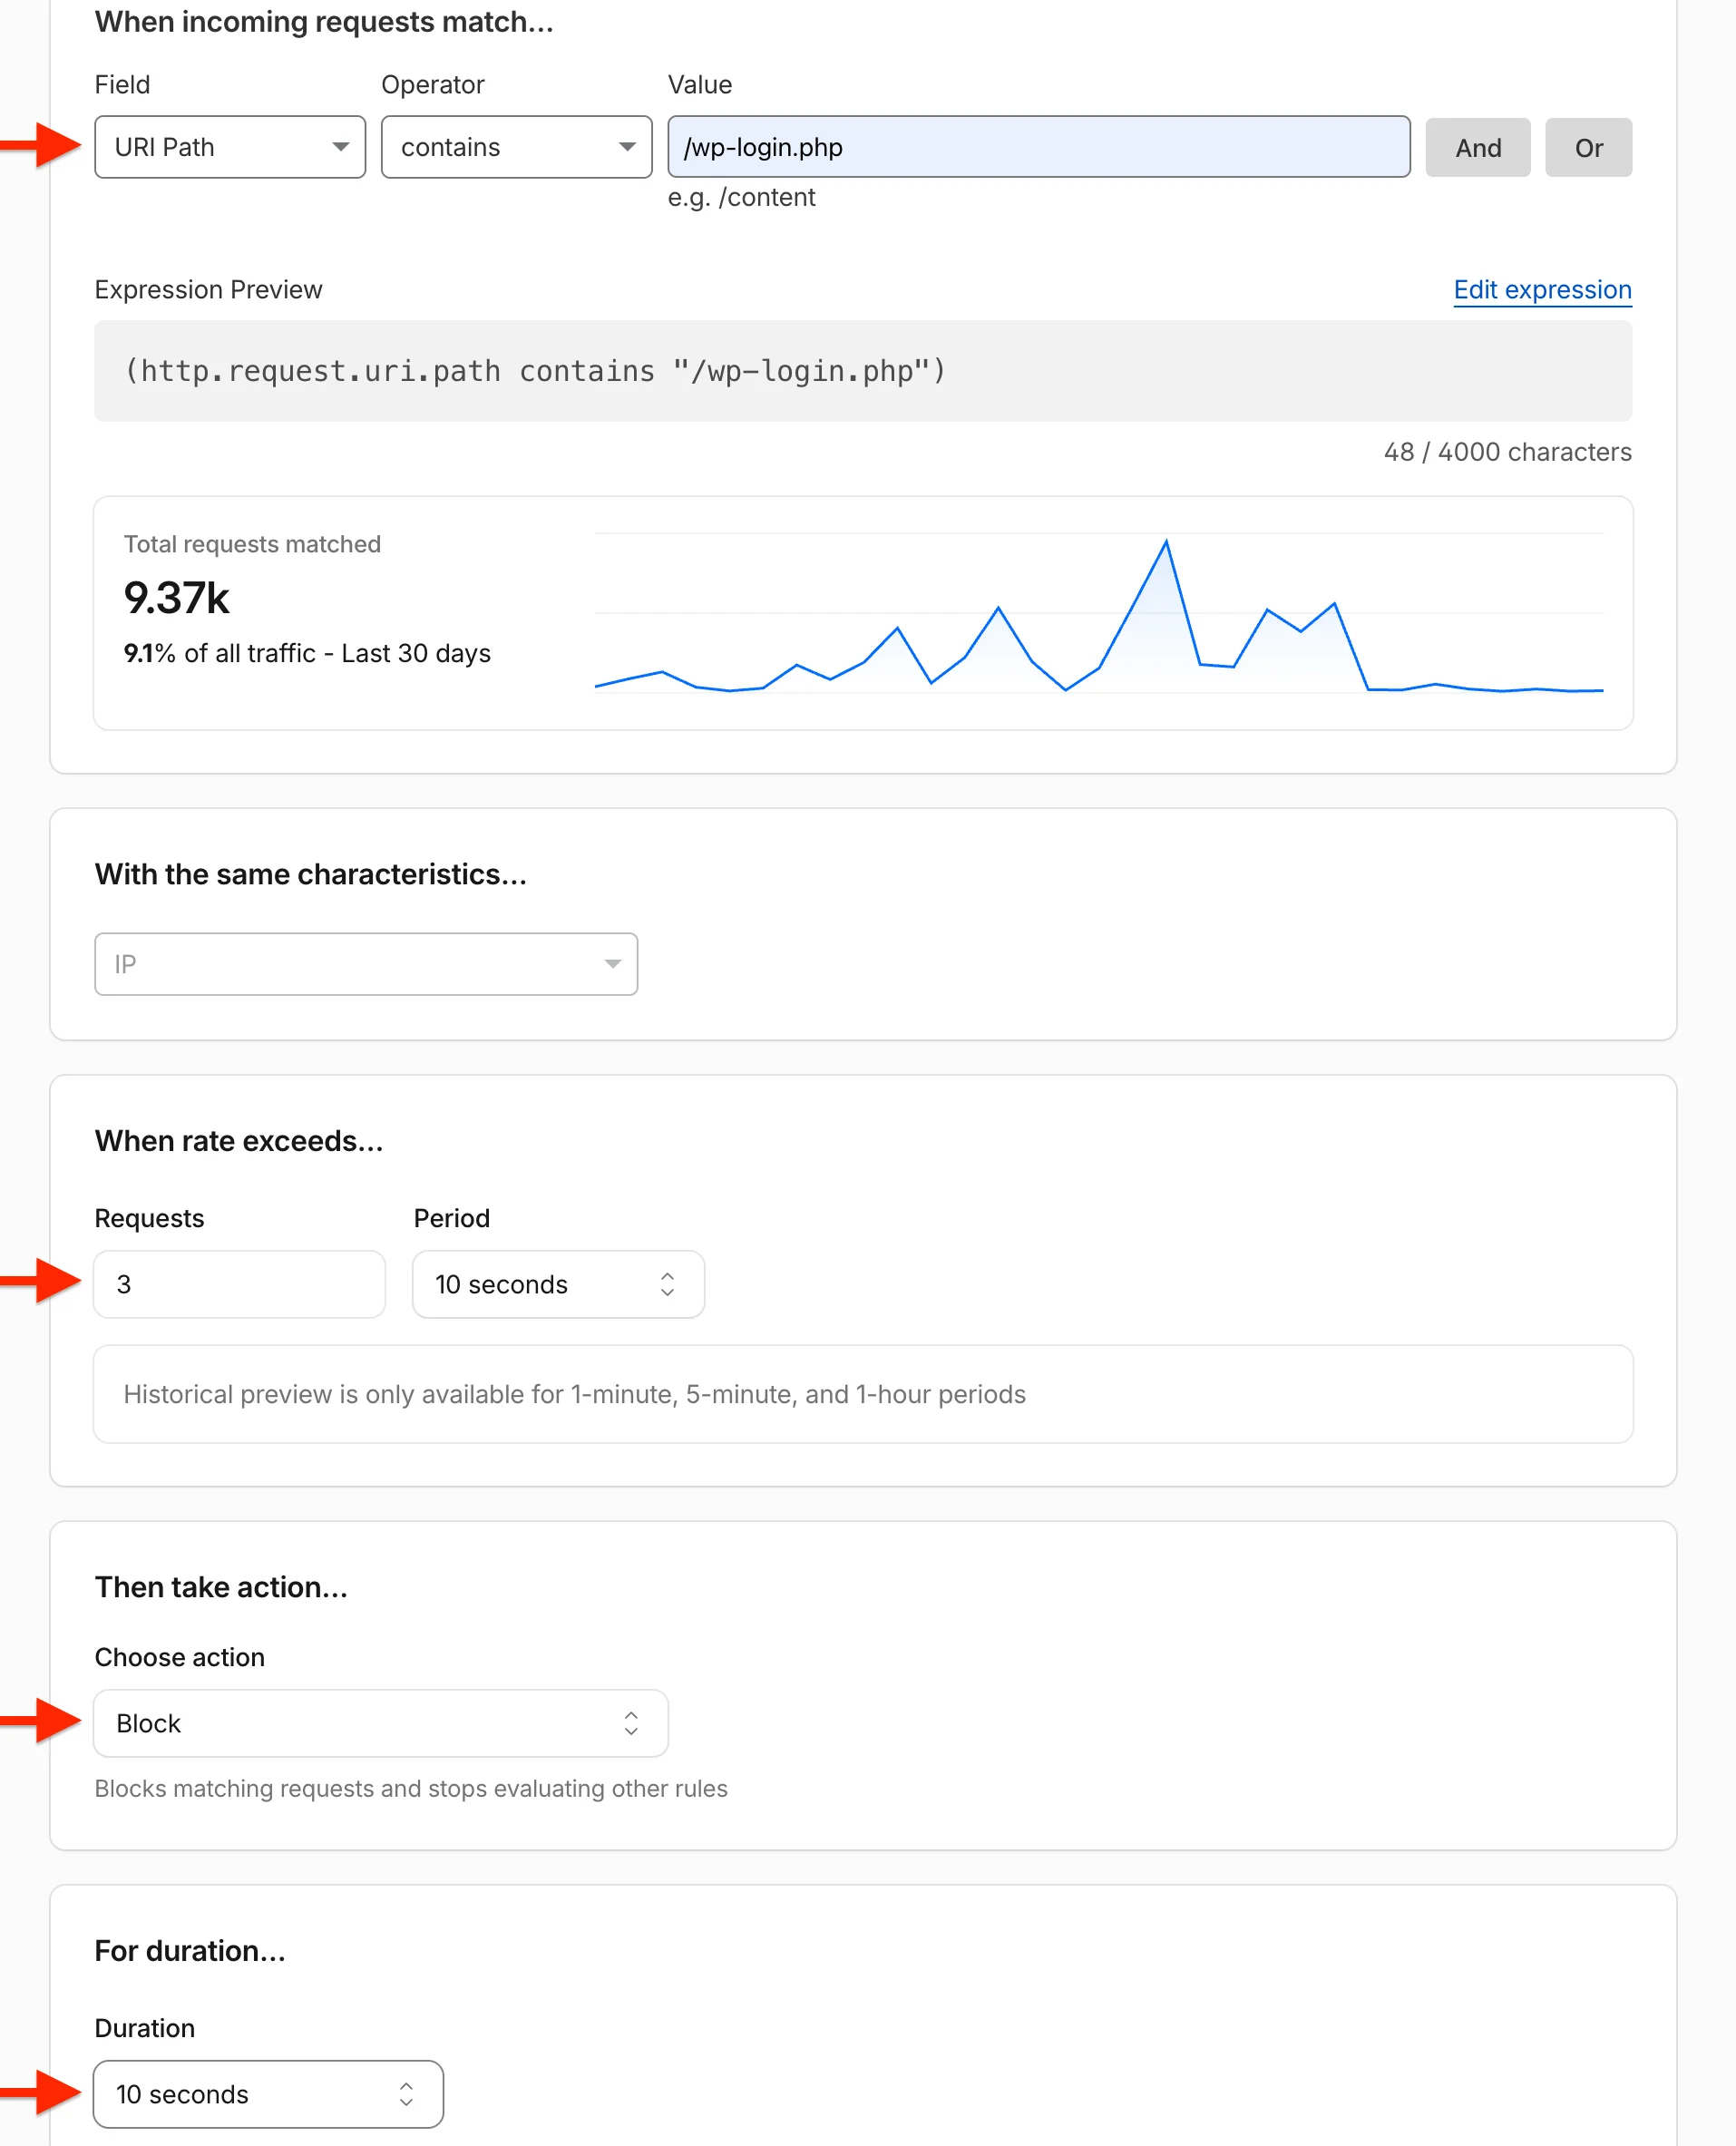
The wp-admin area is a common target for brute-force login attempts. Rate limiting helps you stop attackers from hammering your login form, thus using unnecessary CPU resources.
Steps:
- Go to Security > Security Rules
- Click Create a Rate Limiting Rule
- Rule name: Rate Limiting
- URI Path > contains >
/wp-login.php - Requests: 3 (adjust this if necessary)
- Period: 10 seconds
- Choose action: Block
- Duration: 10 seconds
- Click Deploy to save.
Conclusion
With these extra layers of security, your WordPress site becomes much harder to target, especially for automated attacks.
Your server no longer has to respond to an endless flood of bot requests. This saves precious server resources and can help you lower your hosting costs.
Combined with full-page caching at the edge, your site stays fast for real visitors, even when bots are knocking at the door.
Best of all, you can set up everything in this guide on Cloudflare’s free plan.
Need help setting up Cloudflare?
At WP Fix Fast, Cloudflare setup is included in all our WordPress Support Plans. Let our experts handle it for you. Quick, secure, and stress-free.